Golden SAML attacks bypass MFA by stealing identity provider certificates
Attackers impersonate any user in federated environments by forging tokens with stolen signing keys, rendering password resets and multi-factor authentication ineffective
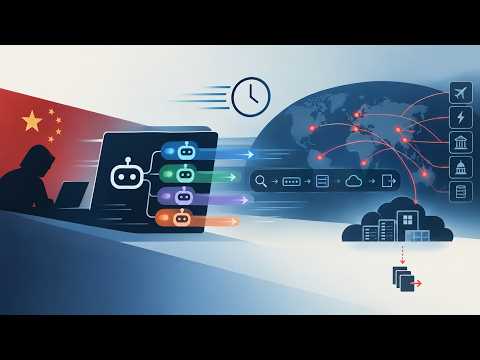
Security firm Wiz identified Storm-0940 using an autonomous penetration-testing framework to probe Okta, Entra ID, and Cognito across software vendors...
The tool correlates EDR telemetry with Okta, Entra ID, and Active Directory to trace attacks from initial endpoint compromise to privilege escalation.
A Semperis report shows identity systems are targeted in 87% of ransomware attacks, highlighting critical gaps in hybrid architectures and recovery ba...
The group has targeted critical infrastructure across four continents since August 2024 using password theft and five specific software vulnerabilitie...
Okta, ServiceNow, and four other vendors have released agent identity tools while the IETF's primary token-exchange draft is set to expire in November...
Five vulnerabilities affecting all versions of industrial network devices risk disrupting energy, healthcare, and government services worldwide, accor...
4 reports
4 reports
4 reports
1 report